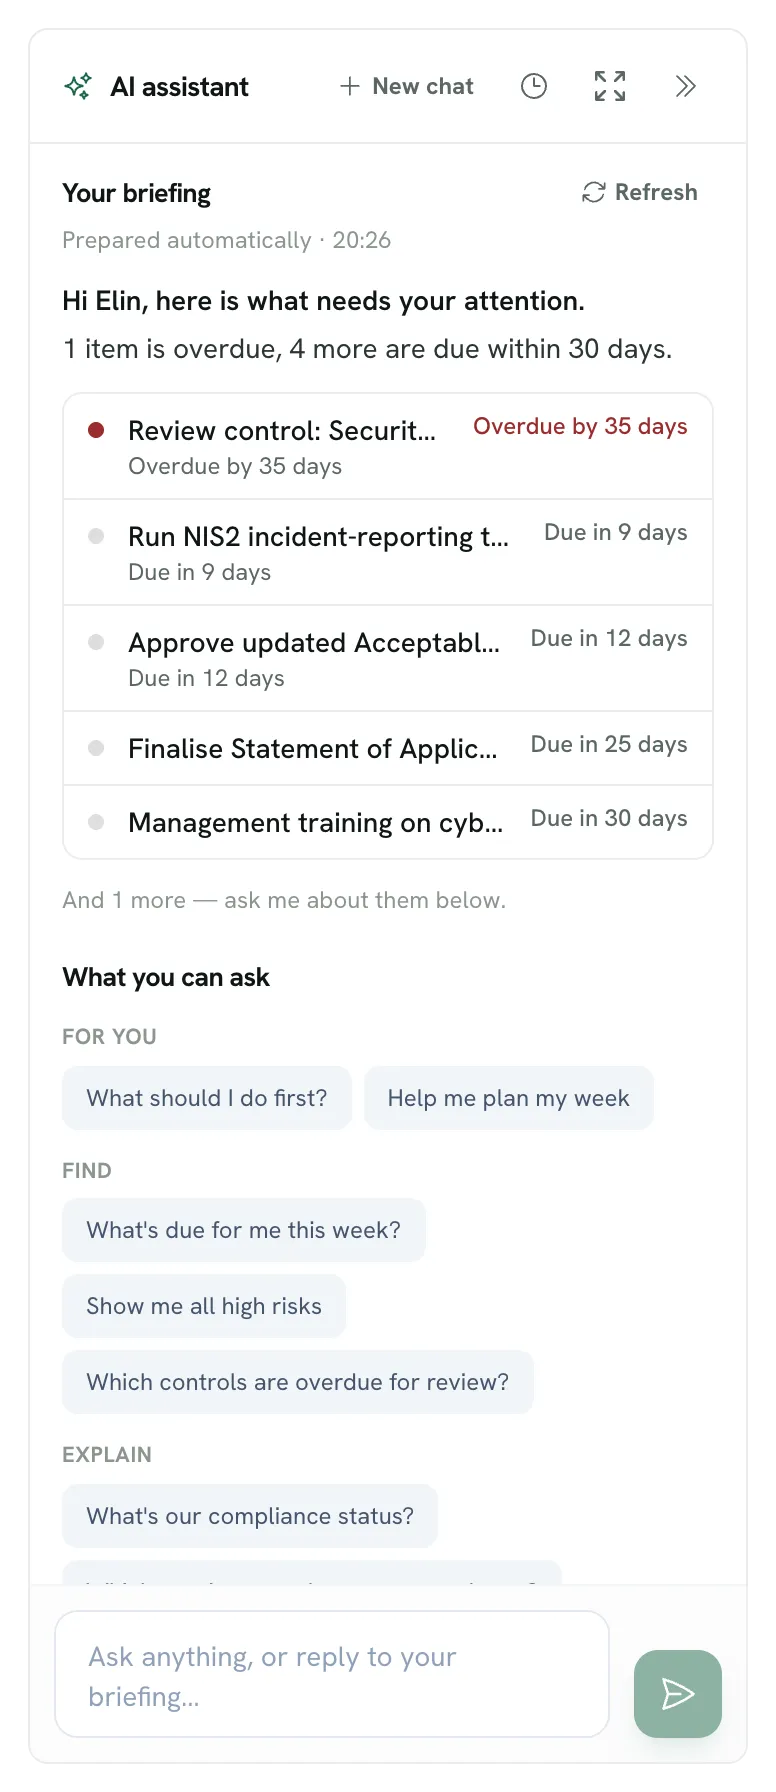
The assistant, inside the product
It sits beside every page, signed in as you, with a briefing built from what is due for you. It reads and changes records through the same API as you, with your role.
Security and controls
Built in Göteborg, hosted on Google Cloud in the EU, with AI on EU-hosted models. Every layer, from sign-in to storage, is designed to keep your data yours.
The short version of our customer security white paper. Ask us for the full one.
01EU-based
Your data, and the AI that works on it, stay in the EU. Here is what runs where.
02Access
Every request is checked on the server, and roles decide what each person can see and do.
On the Enterprise plan, connect your own identity provider over SAML or OIDC, set up per organisation.
Every user can turn on TOTP multi-factor authentication with backup codes, on every plan.
Admins manage users and settings. Members work with the organisation’s records. Auditors can be given read access.
Sessions are verified on every request, and sign-in is protected against password guessing and credential stuffing.
03Your data
Your records are encrypted at rest and in transit, and every query is scoped to the organisation that asks.
AES-256 for the database and every stored file.
TLS 1.2 or later, HTTPS only, everywhere.
Every record and file belongs to one organisation, and access is checked against it on every request.
Automated tests that try to reach another organisation’s data run on every code change.
04Resilience
Fidureon runs on managed Google Cloud services in the EU, spread across data centres, with backups you can restore to the minute.
The application and database run across several zones in the region, and a standby database takes over automatically.
The database has no public access and is reachable only over private connections.
The database is backed up every day, and can be restored to any moment in the last 7 days.
Evidence files are versioned and copied every day to Stockholm, for disaster recovery.
05How we build and run it
Every change is reviewed and scanned before it ships, and production is monitored, with alerts to the operations team.
Found a vulnerability? Read our disclosure policy.
Every change is reviewed, and automated checks scan dependencies, code and containers before anything reaches production.
Credentials live in a managed secret store, and each one is open only to the service that needs it.
The whole platform is defined in code, so every change is reviewed, versioned and reproducible.
Sign-ins, data access and system events are logged, and alerts reach the operations team.
Every change to a record is tracked, with who made it and when.
If an incident affects your data, we tell you, and share the relevant findings.
06AI and MCP
The assistant and the AI tools you connect over MCP go through the same sign-in, role checks and organisation scoping as everything else in Fidureon. Agents work inside your organisation’s data, at the autonomy you set.
Where the AI runs The AI runs on models hosted in EU data centres: Google’s models on Vertex AI in the EU, and selected flows on Mistral, a European AI company.
It sits beside every page, signed in as you, with a briefing built from what is due for you. It reads and changes records through the same API as you, with your role.
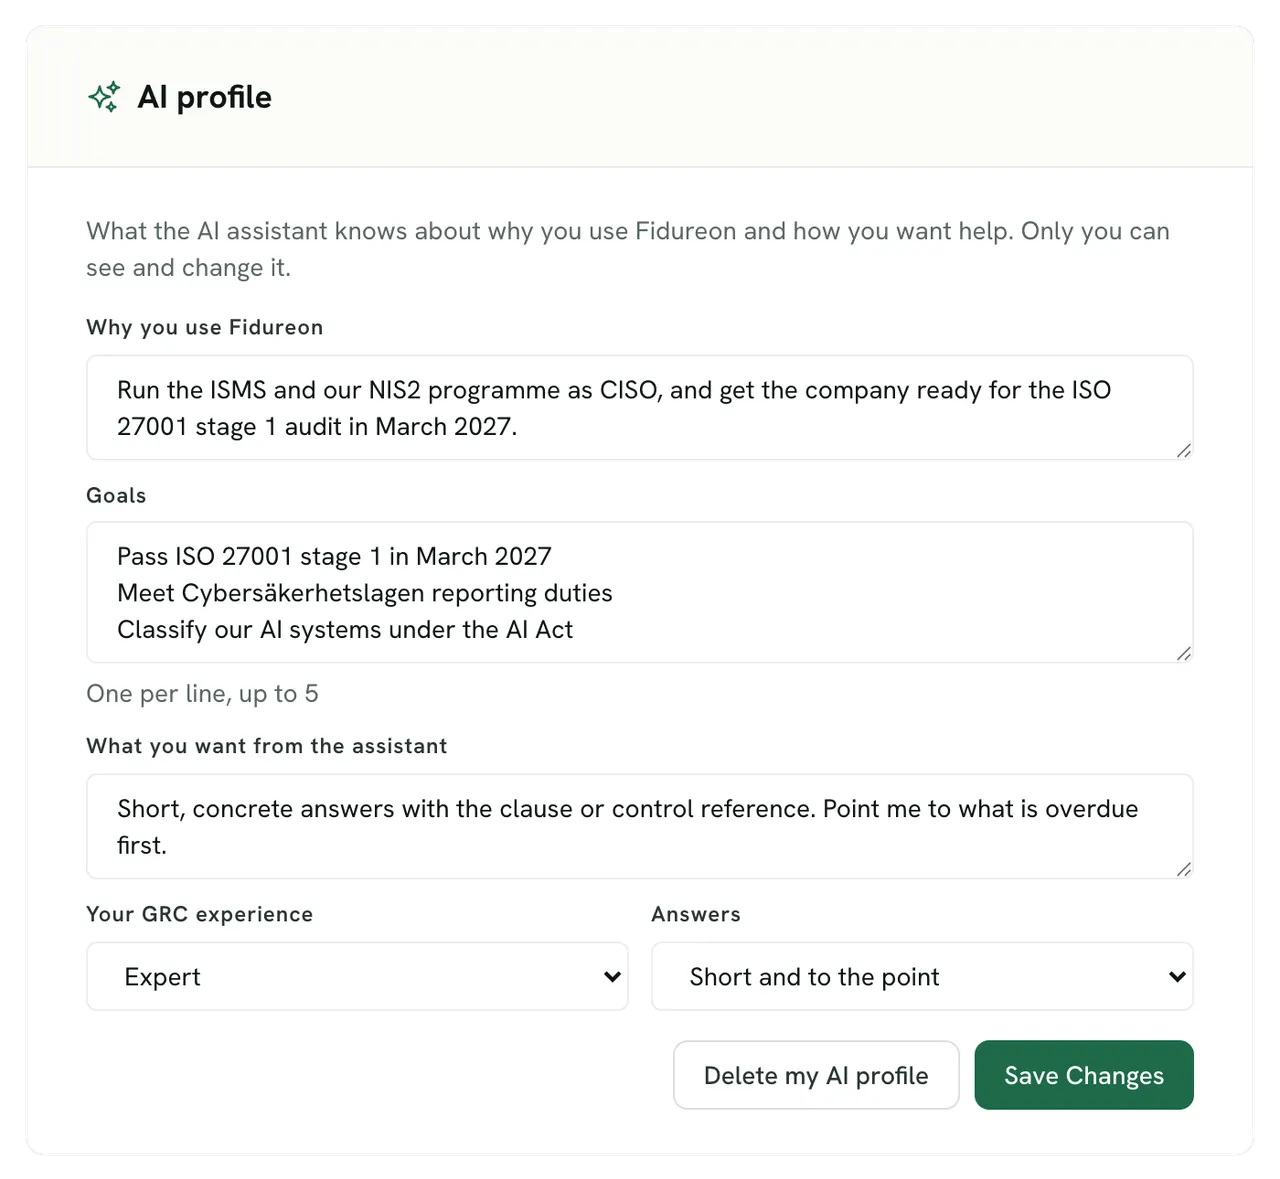
An admin-edited organisation profile and each person’s own AI profile shape the answers. Only you see yours, and you can change or delete it at any time.
Real product views, captured with a fictional demo company.
AI risk managementCShift AB works in line with the EU AI Act: every AI model in Fidureon goes through a structured risk analysis of its purpose, the data it handles and its impact, with oversight and transparency measures to match.
07Compliance
Fidureon is built and run in line with the same frameworks it helps you meet.
CShift AB runs its information security management in line with ISO 27001:2022, covering how we build, run and support Fidureon.
Fidureon’s own security controls are mapped and assessed against all 93 Annex A controls.
We process your data as your processor, under a data processing agreement, and support data subject rights including deletion.
Every AI model in the platform is risk-assessed. For your own AI systems, the product has an AI register.
Your organisation’s data can be exported at any time, in a common machine-readable format.
The Minimum Viable Secure Product checklist is our baseline for enterprise-ready B2B security.
The white paper
Our customer security white paper covers each part of this page in more detail, for your vendor assessment, procurement or audit. Ask for it and we send it to you.
Or write to [email protected]
FAQ
Hosted in Google Cloud europe-north1 (Finland), with a daily copy of evidence files in europe-north2 (Stockholm). Database backups stay in Google Cloud’s EU locations.
The AI runs on models hosted in EU data centres: Google’s models on Vertex AI in the EU, and selected flows on Mistral, a European AI company. The assistant and agents work with the same sign-in, role checks and organisation scoping as the rest of Fidureon.
Yes. SSO over SAML or OIDC is on the Enterprise plan, and every user on every plan can turn on TOTP multi-factor authentication with backup codes.
Yes. In line with the EU Data Act, your organisation’s data can be exported at any time, in a common machine-readable format.
Yes, through Fidureon’s MCP server. Your admins create API keys scoped to your organisation, every request goes through the same checks as the app, and key use is logged and rate-limited.
Yes. We sign a data processing agreement with every customer, and it includes the full list of sub-processors.
Yes. Email [email protected] for the customer security white paper, or to set up a security review with our team. To report a vulnerability, use the same address; our vulnerability disclosure policy explains the scope and how we respond.
We walk through hosting, access and AI with your security team, using your own frameworks. Or start with the free readiness check for ISO 27001 or the EU AI Act.