The frameworks Europe asks for. In one platform.
Seven regulations and standards on one shared set of controls, evidence and actions.
The seven
What ships for each framework.
Counts come straight from the product. Switch on the frameworks you need.
Laws and regulations
Whether one applies depends on your sector, size and role.
-
EU AI Act
Regulation (EU) 2024/1689
Obligations phase in from 2025 to 2028. Check the official timeline.
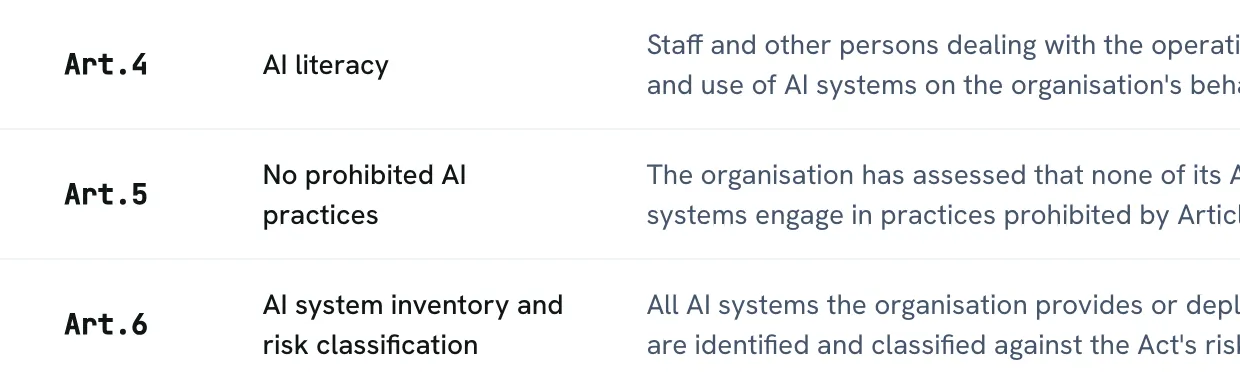
- readiness requirements
- 23
- risk tiers
- 4
-
GDPR
Regulation (EU) 2016/679
Your supervisory authority can ask for your Article 30 records.
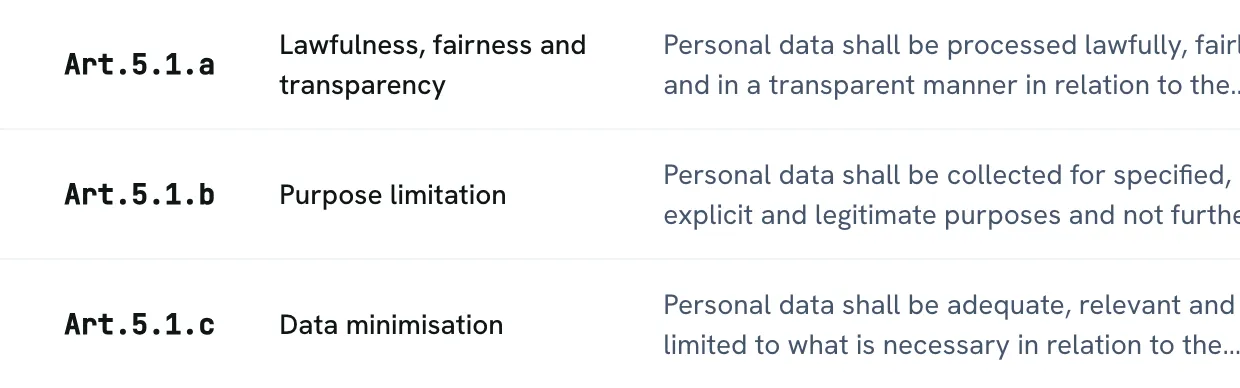
- requirements
- 40
- assessment types: DPIA, LIA, TIA
- 3
-
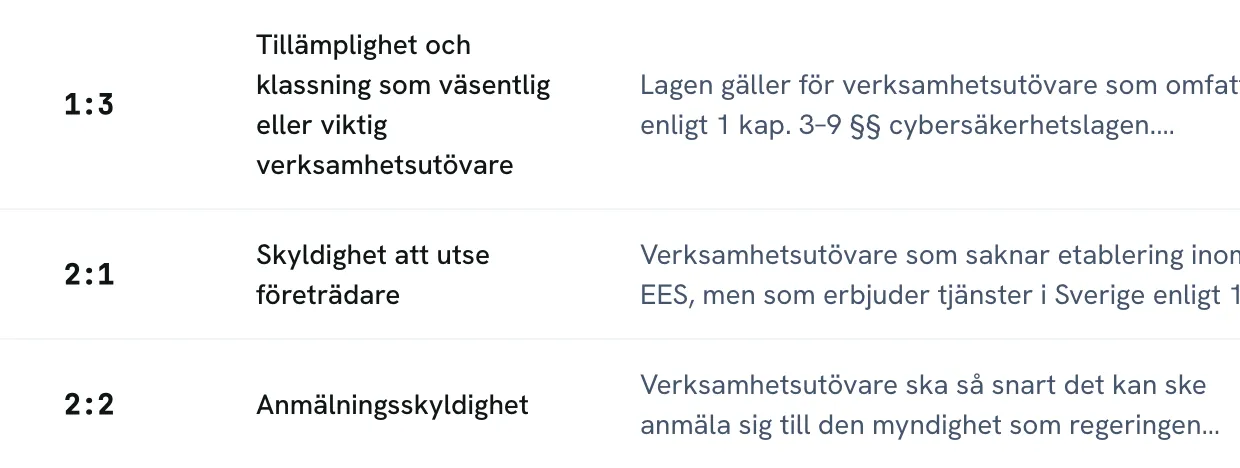
NIS2 (Sweden)
Swedish Cybersäkerhetslagen
Cybersäkerhetslagen is in force from 15 January 2026.
- Cybersäkerhetslagen requirements
- 25
-
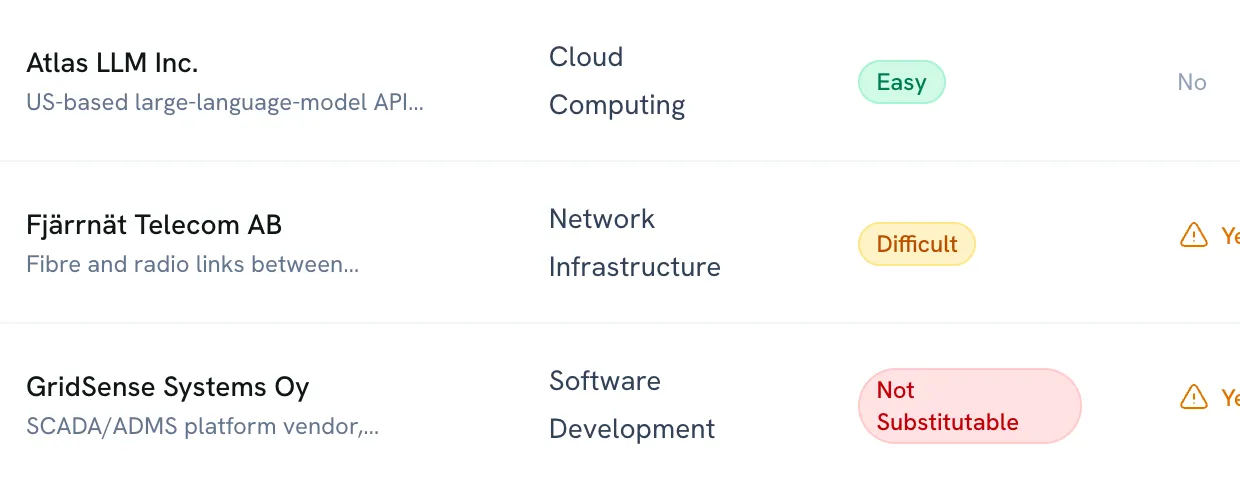
DORA
Regulation (EU) 2022/2554 · feature module
Financial entities must keep a Register of Information on ICT providers.
- core Register of Information templates
- 4
ISO standards
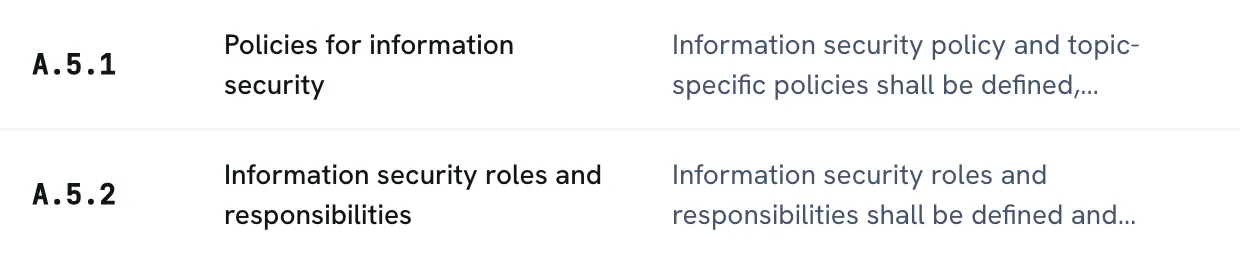
Certifiable management systems. An accredited body does the certifying.
Also available to switch on
- CRA (50 requirements)
- EU Data Act (24 requirements)
- PCI DSS 4.0.1 (246 requirements)
- TISAX (80 requirements)
- MVSP (25 requirements)
- custom frameworks of your own
One workspace
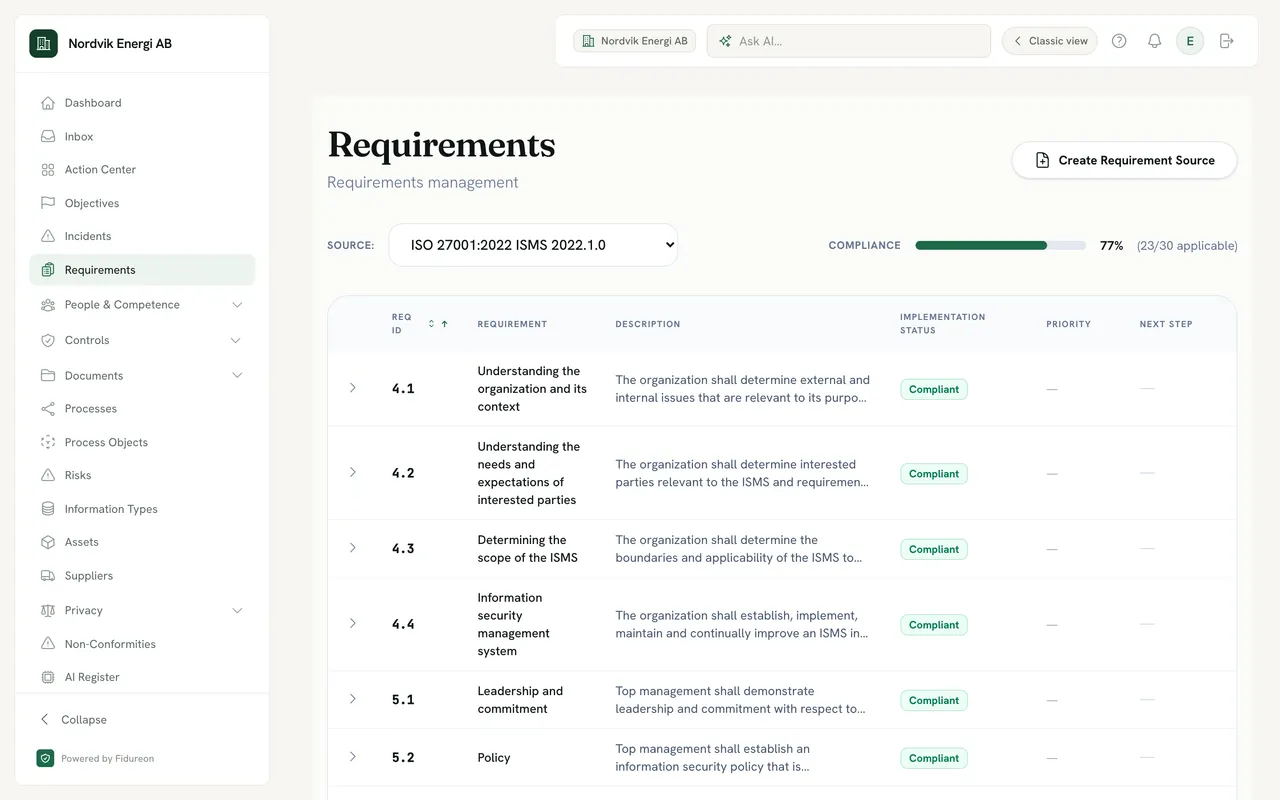
One requirements view. Every framework.
The view at the top of this page works for every framework. Switch the source and it lists another catalogue, with its own compliance figure.
-
A catalogue per framework
Clauses for the ISO standards, articles for GDPR and the EU AI Act, and the requirements of Cybersäkerhetslagen in Swedish. Each requirement carries a status from the work linked to it.
-
Link a control once
Frameworks overlap, so you link a control to every requirement it meets, by hand or by accepting AI suggestions when you import controls. Its actions and evidence then count toward each.
-
DORA as a module
DORA is not a list in this view. It ships as a module: the ICT third-party register, critical functions, exit strategies and an export of the 4 core Register of Information templates.
Groups and subsidiaries
Every subsidiary on the frameworks it needs.
Build your group as an entity tree, mandate frameworks from the parent and add NIS2 (Sweden) only where it applies.
Mandated from the parent
Choose a framework at group level and put it in scope on the subsidiaries you pick.
Each company’s own figure
Every subsidiary tracks its own progress, and you compare them side by side.
A trend per entity
Weekly snapshots show how each company’s readiness has moved.
Each entity also gets its own admins and invites, and group policies can be shared read-only down the tree.
Where to start
Find the frameworks that fit you.
A starting point, not legal advice: whether a law applies depends on your sector, size and role.
-
You build, buy or use AI systems
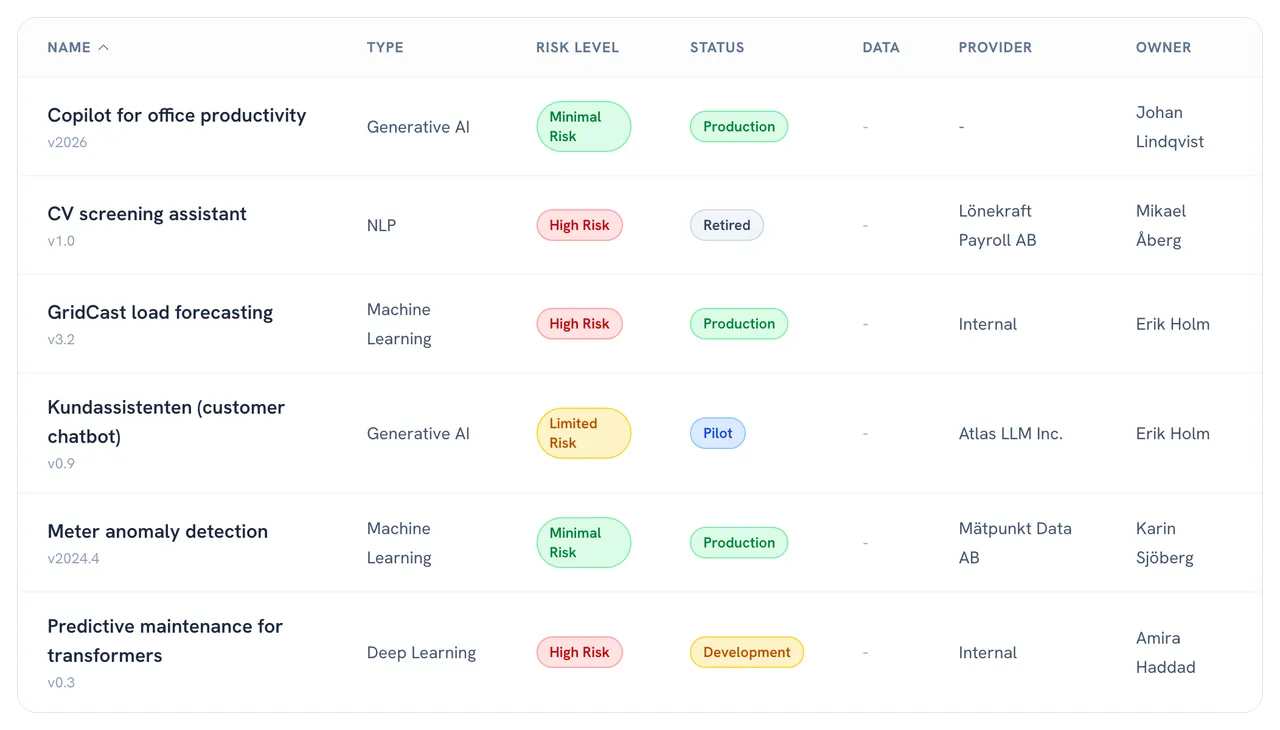
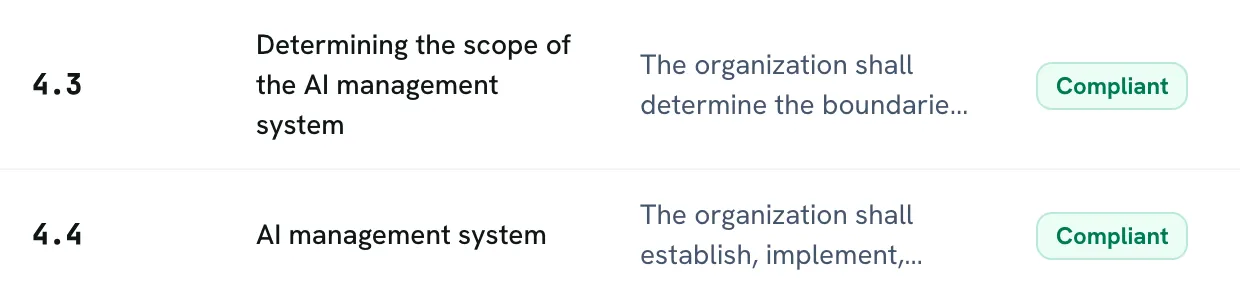
One AI register for both: risk tier and role for the EU AI Act, plus the 38 Annex A controls of ISO 42001.
-
You process personal data
Keep the Article 30 register current and run DPIAs, LIAs and TIAs with autofill and AI drafts.
-
You are an essential or important entity in Sweden
Work through the 25 requirements of Cybersäkerhetslagen, with risk, supplier and incident work alongside.
-
You are a financial entity in the EU
Run the ICT third-party register, map critical functions and export the 4 core Register of Information templates.
-
Your customers ask for a certificate
Prepare for ISO 27001 with all 93 Annex A controls and an SoA, or for ISO 9001 with non-conformities and CAPA.
-
Not sure yet
Start with the free readiness check for ISO 27001 or the EU AI Act, or book a demo to walk through your scope.
FAQ
Framework questions.
Which frameworks does Fidureon support?
Seven key frameworks: the EU AI Act, GDPR, NIS2 through Sweden’s Cybersäkerhetslagen, DORA, ISO 27001, ISO 42001 and ISO 9001. Also available: CRA, EU Data Act, PCI DSS 4.0.1, TISAX, MVSP and custom frameworks of your own. You switch on the frameworks you need for your organisation.
Do we have to do the same work again for each framework?
No. A control in Fidureon can be linked to requirements in several frameworks at once, so its actions and evidence count toward each of them. You make the links yourself, or accept AI suggestions when you import controls from documents or spreadsheets.
Which NIS2 law does Fidureon cover?
Sweden’s Cybersäkerhetslagen, with 25 requirements. For another country’s requirements, add them as a custom framework and link the controls you already run to them.
How does Fidureon cover DORA?
As a module for ICT third-party risk and operational resilience: the ICT third-party register, critical-function mapping, exit strategies, resilience gaps and an export of the 4 core EBA Register of Information templates.
When do EU AI Act obligations apply?
They phase in from 2025 to 2028. Check the official timeline for the obligations that apply to your role. In Fidureon you can start now: register your AI systems, classify their risk tier and work through the 23 readiness requirements.
Can we add our own framework?
Yes. You can add custom frameworks and custom requirements, such as internal policies or customer demands, and link your existing controls to them like any other framework.
Does Fidureon certify us?
No. Certification against ISO 27001, ISO 42001 or ISO 9001 is done by an accredited certification body. Fidureon is where you prepare: requirements, Statement of Applicability, controls, evidence and gap analysis reports for your audit.
See your frameworks in Fidureon.
Book a demo and we will walk through the frameworks on your list with your own scope. Or start with the free readiness check for ISO 27001 or the EU AI Act.