Does Fidureon certify us for ISO 27001?
No. An ISO 27001 certificate is issued by a certification body, usually an accredited one, after its own audit. Fidureon is where you build and run your information security management system, record your Statement of Applicability and keep the evidence, so that you are ready when the auditor arrives.
Which version of ISO 27001 does Fidureon cover?
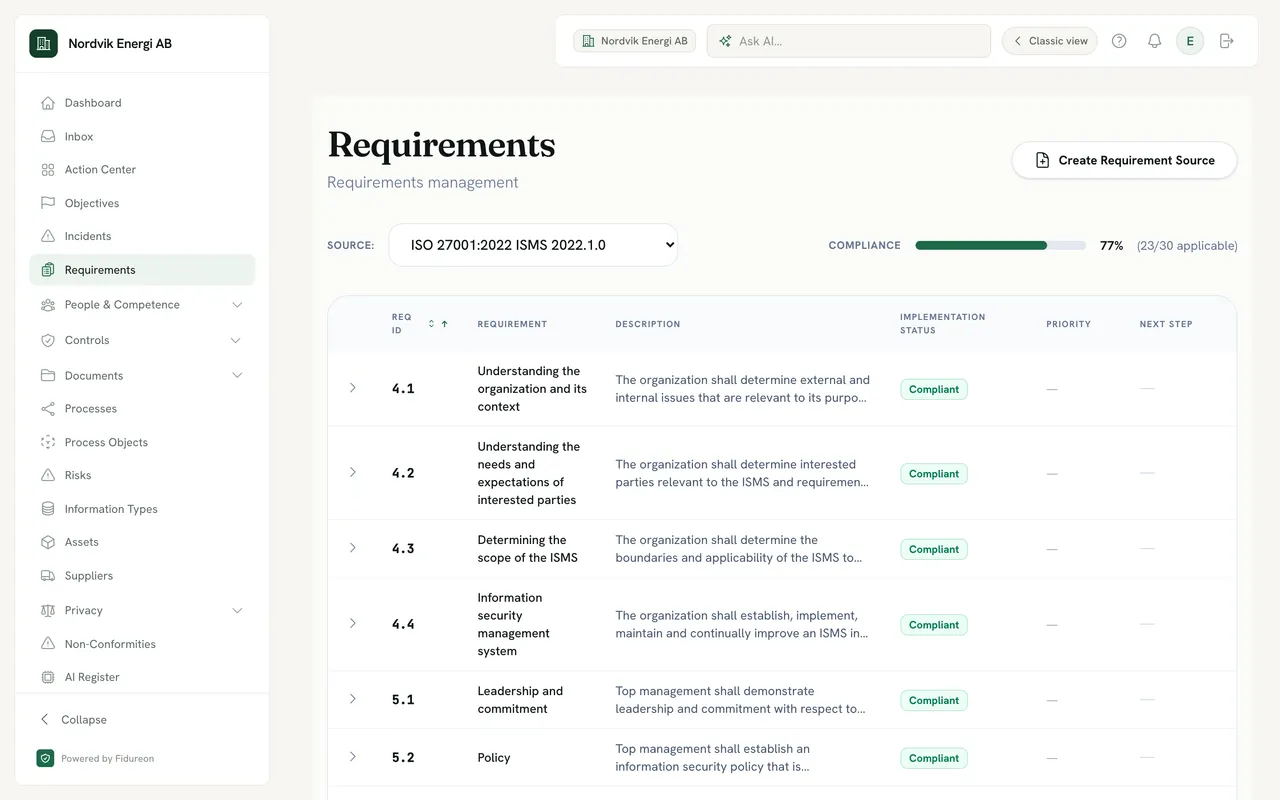
ISO/IEC 27001:2022, the current edition: 30 requirements across clauses 4 to 10 and all 93 Annex A controls, grouped in the four themes organisational, people, physical and technological.
How does the Statement of Applicability work?
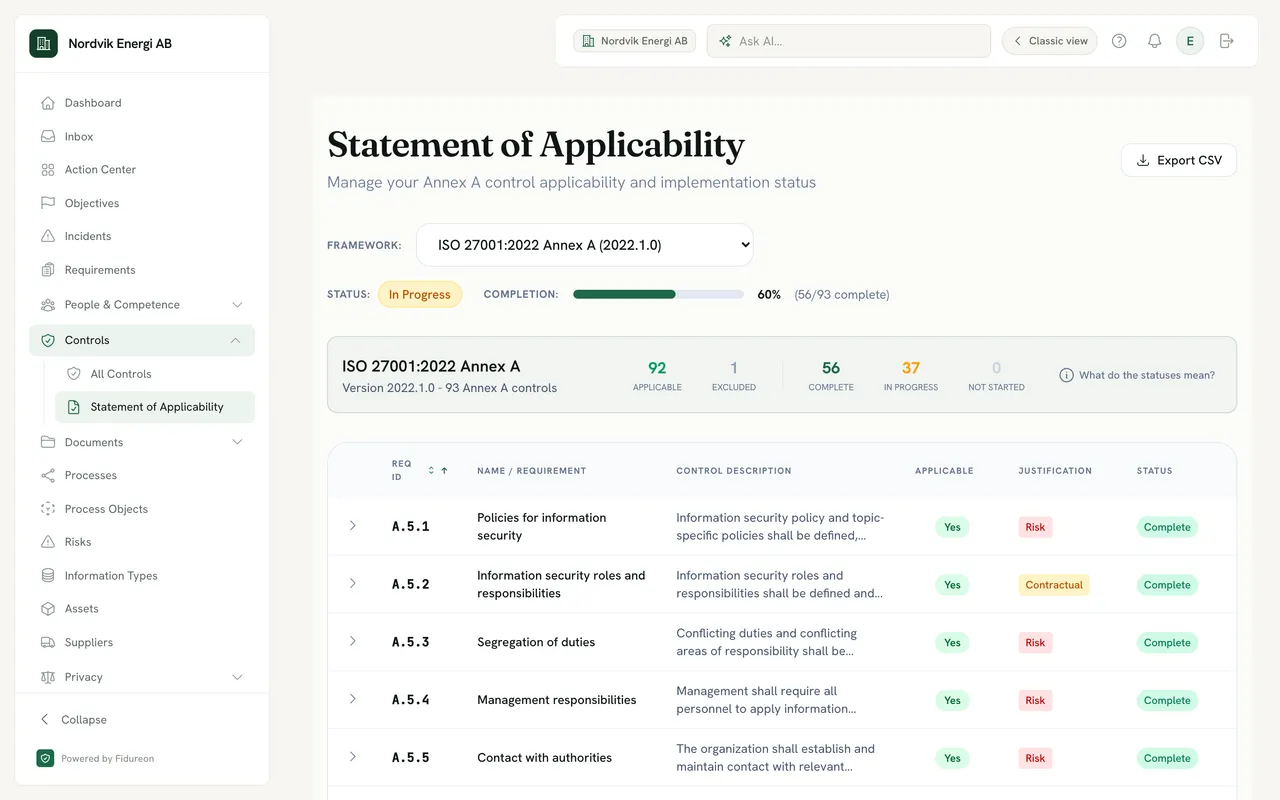
Each Annex A control is marked applicable or not applicable, with a justification and a justification type: security baseline, risk, regulatory, contractual. In the readiness check, six risk-profile questions mark the controls that are clearly out of scope as not applicable, using fixed rules, not AI; every other control stays applicable, and you can change any decision. The Statement of Applicability exports to CSV.
Does Fidureon help with the asset inventory (A.5.9)?
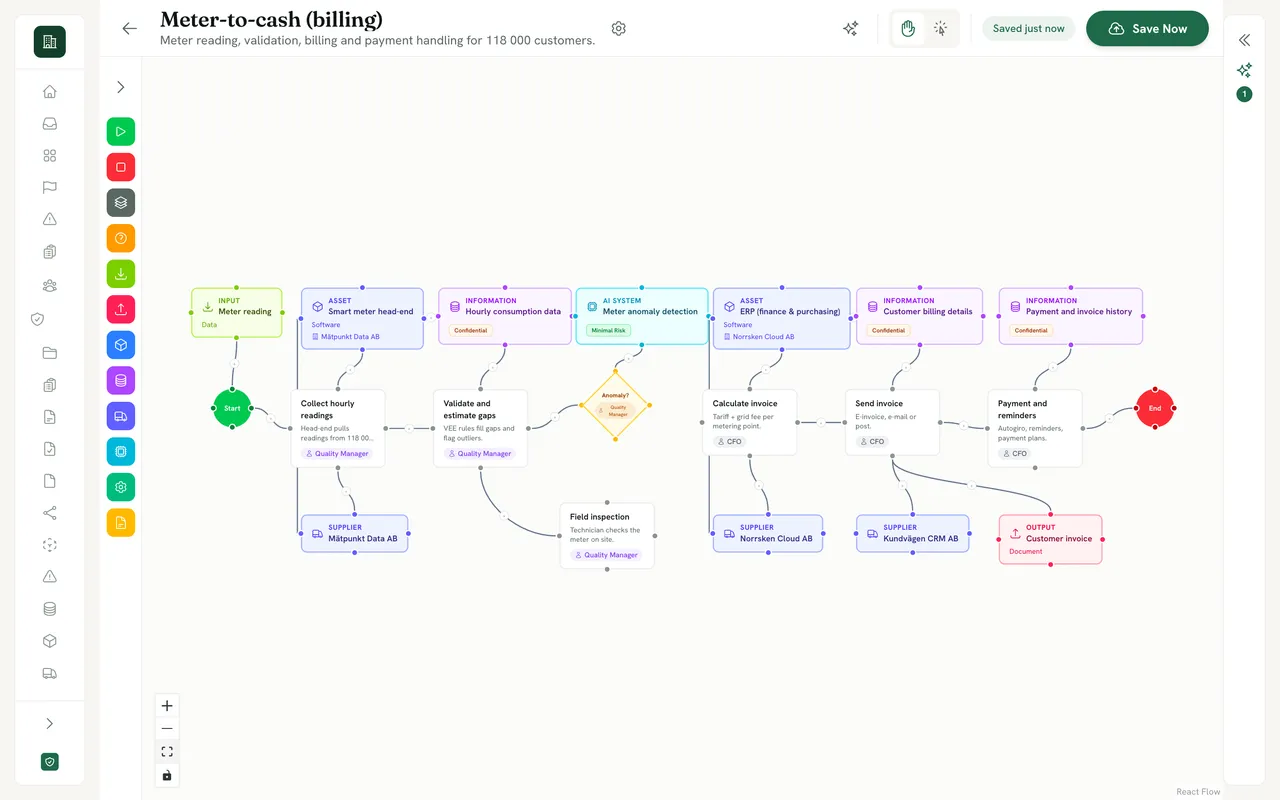
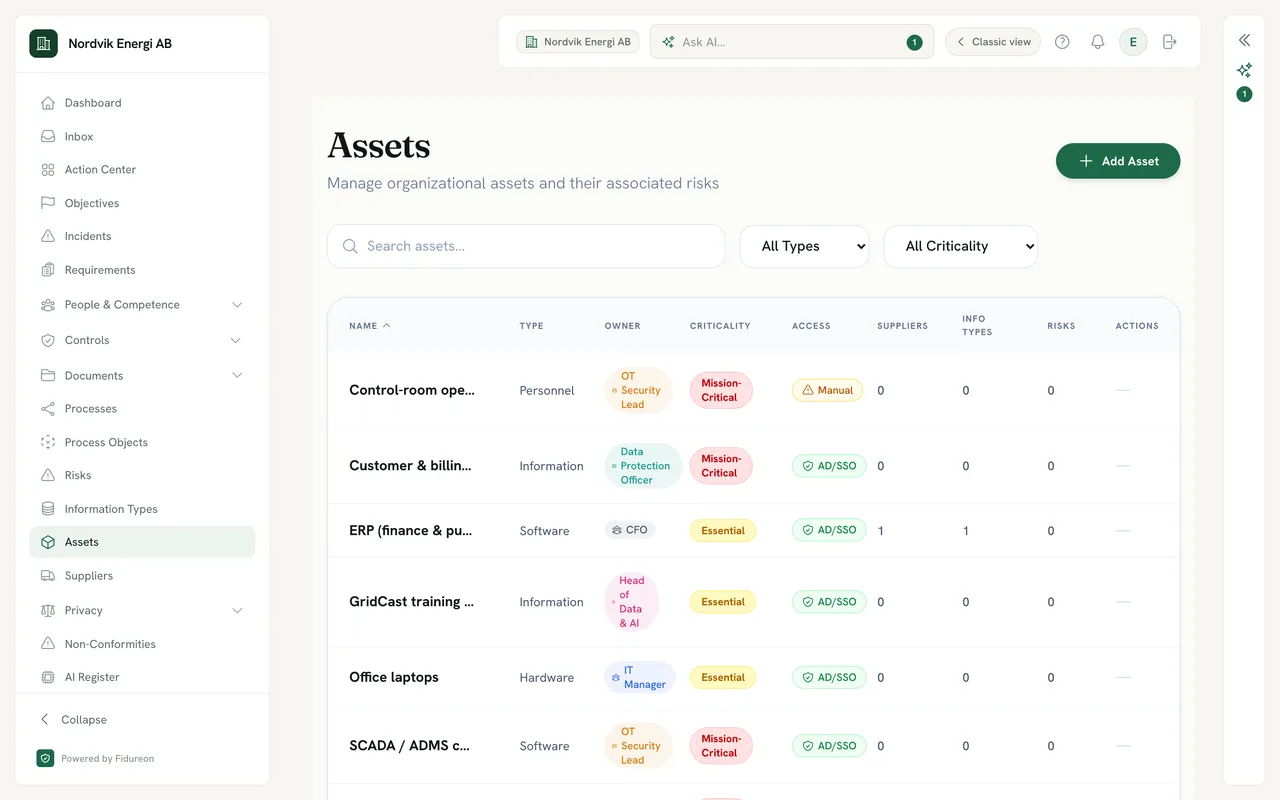
Yes. You keep assets, information types with their classification, and suppliers in registers. On the process canvas you draw how a process runs, add the records each step uses, and create new ones right there with Create & Link. When you save, Fidureon links the process to those records, and the connections on the diagram link assets to their information types and suppliers, so the asset register shows them. Drawing alone never creates register entries.
What is the free readiness check?
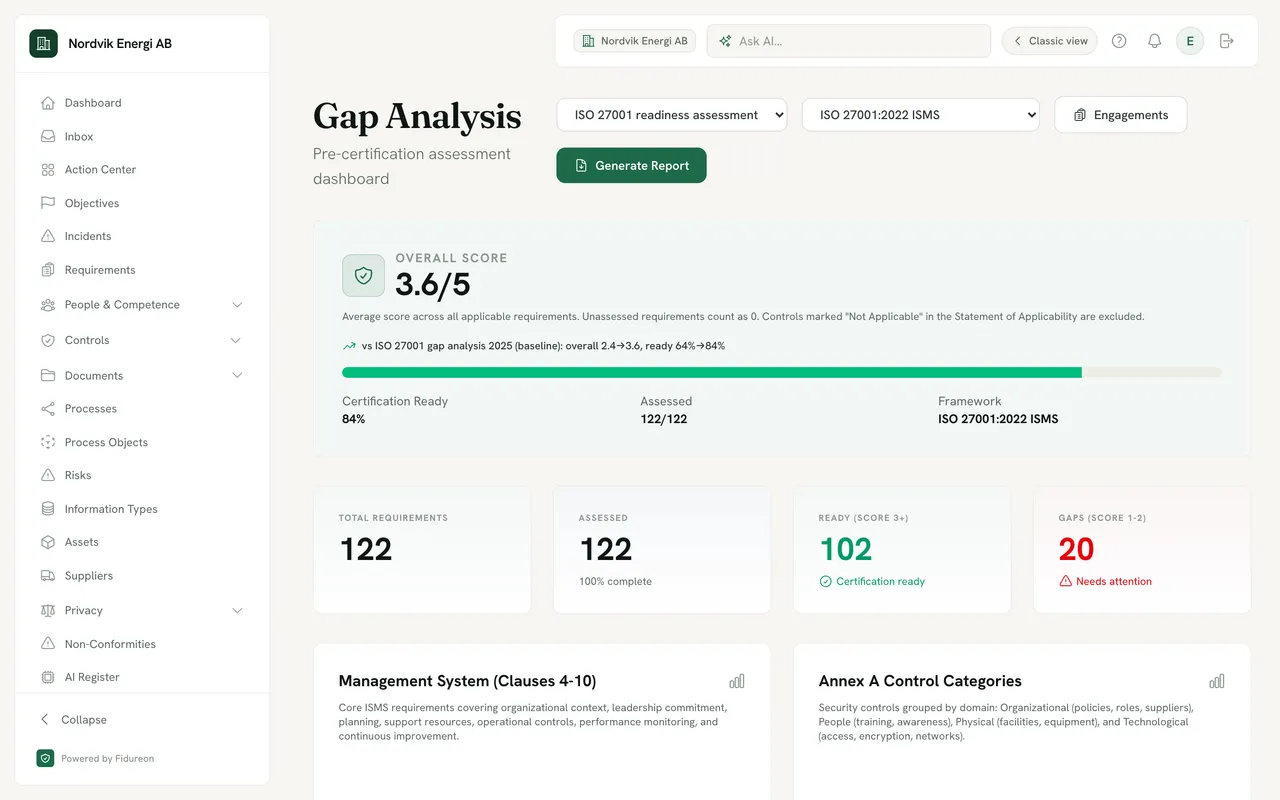
A guided, chat-led assessment in the Fidureon app. ISO 27001 is its default track; the other track is the EU AI Act. You upload the documents you already have, Fidureon proposes a score for each requirement, and a person reviews and approves every proposed score. You end with a readiness score and a list of gaps.
Can Fidureon collect evidence automatically?
From GitHub, yes. In the readiness check, the GitHub connector reads configuration from your most active repositories, such as branch protection and required reviews, CODEOWNERS, CI workflows, vulnerability alerts and secret scanning, and turns it into proposed scores that you approve. Other evidence, such as policies and records, is uploaded or written in Fidureon.
Can we reuse our ISO 27001 work for NIS2 (Sweden) or GDPR?
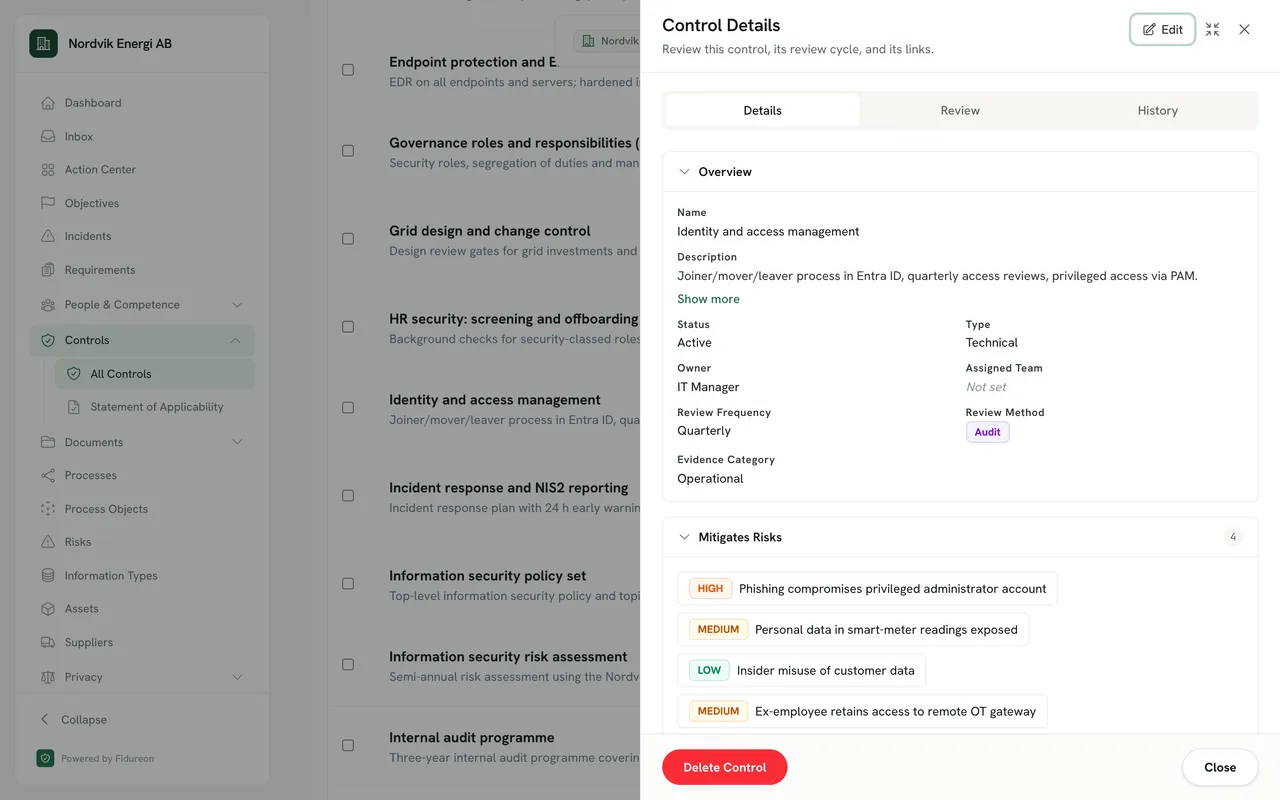
Yes. A control can be linked to requirements in any framework you have active, such as GDPR, NIS2 (Sweden) and ISO 42001, so the same control and its evidence count toward each of them. You make the links yourself, and Fidureon suggests them when you import controls from documents or spreadsheets.
Where is our ISMS data hosted?
Fidureon is built and operated by CShift AB in Göteborg and hosted on Google Cloud in the EU: europe-north1 (Finland) is the primary region, and evidence files are replicated every day to europe-north2 (Stockholm). The AI runs on models hosted in EU data centres: Google’s models on Vertex AI in the EU, and selected flows on Mistral, a European AI company. The security page has the details.